Cloudflare Ignite Consumer ISP Confusion with BGP Safety Test
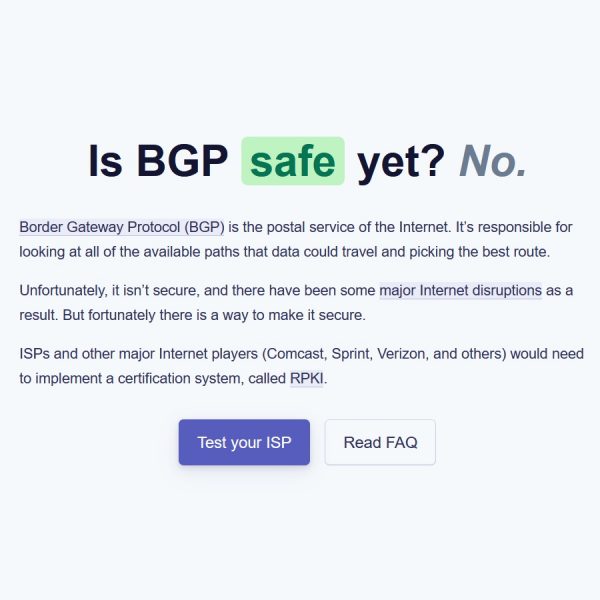
Over the past few days we’ve had a small but growing stream of Tweets and Emails from people who have run Cloudflare’s new ‘Is BGP Safe Yet‘ tool and are worried that their UK broadband ISP is “unsafe” because it uses the Border Gateway Protocol (BGP) and not RPKI. Aside from poor timing with COVID-19, the result can be misleading.
The Border Gateway Protocol (BGP) system is a protocol that helps to link the internet together by exchanging routing information with Autonomous Systems (AS), such as those run by your ISP (each provider will have many peers and routes to send data). Networks around the world need to talk to each other in order to do peering and determine which routes are the best ones for them to send their data, which is what BGP facilitates.
BGP is normally one of those things that works seamlessly in the background and there are a lot of very technical aspects to it, which is just one of many reasons why launching an oversimplified checking tool – seemingly aimed at ordinary non-tech savvy consumers – could be counter-productive. Likewise doing this during a global pandemic, when network operators have much bigger problems to focus on, doesn’t seem terribly helpful.
Advertisement
The risk is that some people may assume that what the website is telling them is the only truth and become concerned for their online security (a fact born out by the messages we’ve recieved). Indeed at present most ISPs will probably return results like the ones below from UK providers, which Cloudflare then asks you to spam spread via social media as part of their marketing campaign.
FAILURE
Your ISP (Sky Broadband, AS5607) does not implement BGP safely. It should be using RPKI to protect the Internet from BGP hijacks.
FAILURE
Your ISP (THREE UK, AS206067, AS206067) does not implement BGP safely. It should be using RPKI to protect the Internet from BGP hijacks.
FAILURE
Your ISP (Virgin Media Business, AS5089) does not implement BGP safely. It should be using RPKI to protect the Internet from BGP hijacks.
Sadly it is indeed true to say that BGP does have its problems, not least because it relies upon a degree of trust between networks. Sometimes network operators can make mistakes (e.g. human error), which may result in them announcing incorrect routes and that can send a lot of traffic off in the wrong direction, causing all sorts of problems. Similarly other networks may abuse this trust to hijack traffic for malicious purposes.
Over the years various changes and attempts have been made in order to tackle such challenges. One of the most recent is Resource Public Key Infrastructure (RPKI), which as Cloudflare says is a “security framework method that associates a route with an autonomous system. It uses cryptography in order to validate the information before being passed onto the routers.”
Louis Poinsignon, Cloudfare, said:
“BGP leaks and hijacks have been accepted as an unavoidable part of the Internet for far too long. We relied on protection at the upper layers like TLS and DNSSEC to ensure an untampered delivery of packets, but a hijacked route often results in an unreachable IP address. Which results in an Internet outage.
The Internet is too vital to allow this known problem to continue any longer. It’s time networks prevented leaks and hijacks from having any impact. It’s time to make BGP safe. No more excuses.
Border Gateway Protocol (BGP), a protocol to exchange routes has existed and evolved since the 1980s. Over the years it has had security features. The most notable security addition is Resource Public Key Infrastructure (RPKI), a security framework for routing. It has been the subject of a few blog posts following our deployment in mid-2018.
Today, the industry considers RPKI mature enough for widespread use, with a sufficient ecosystem of software and tools, including tools we’ve written and open sourced. We have fully deployed Origin Validation on all our BGP sessions with our peers and signed our prefixes.
However, the Internet can only be safe if the major network operators deploy RPKI. Those networks have the ability to spread a leak or hijack far and wide and it’s vital that they take a part in stamping out the scourge of BGP problems whether inadvertent or deliberate.”
The intention of Cloudflare’s tool, which is to make BGP more secure by encouraging adoption of RPKI, is a noble one but it does seem to be causing some unnecessary panic. Firstly, just to clear up one confusion that has surfaced as a result of this tool, RPKI is a complement to BGP and NOT a replacement (RPKI is effectively a cryptographic wrapper for BGP). BGPv4 remains the primary routing protocol, which even Cloudflare uses.
Advertisement
The next issue is that implementing RPKI is a very complicated task and not the sort of thing a network operator would take on during the COVID-19 pandemic, when the risk of mistakes causing wider problems is one best avoided. A risk assessment and a lot of planning would be needed first because if you haven’t got all your ducks in a row (including peers downstream from you) then blackholing internet traffic becomes a real possibility.
In the meantime it’s probably the wrong time to loudly proclaim that most ISPs are “not secure” simply because they haven’t adopted RPKI yet. Good networks will already filter BGP announcements to ensure that the information they share is correct, although sadly some parts of the world and networks don’t do this, hence how hijacks can become a problem (these are usually rectified quite quickly).
Nevertheless for the most part BGP does its job and major problems are uncommon, if not as rare as we’d all like. As things stand the list of providers who do not yet fully implement RPKI, as shown on Cloudflare’s site, is still far larger than the list of those who do. Major players like Google, Zayo, Level3 (CenturyLink), Vodafone and Comcast have yet to do so.
Otherwise, please don’t panic if your ISP, like most providers, doesn’t yet support RPKI. We suspect that they’ll almost all get around to adopting it eventually but changing such core pieces of a network can take time and a huge amount of care. Right now, when it comes to internet security, the vanilla malware stuff like viruses, phishing, DNS hijacks and SPAM are still a much bigger threat to individual internet users.
Advertisement
The MD of UK ISP Andrews and Arnold (AAISP), Andrian Kennard, has a good blog up on all this (here). “If the major transit providers start filtering routes checking RPKI then that alone will solve the problem of rouge routes – but if they all filter what they receive anyway from customers, that would avoid the issue without RPKI,” said Adrian.
UPDATE 22nd April 2020
We note that Hyperoptic is one of several UK ISPs to have issued brief statements on this after receiving some of the same messages of concern from customers, usually following use of the tool.
HO’s Statement
“We would like to thank everyone for bringing this website to our attention. We understand your concern, but firstly, let us reassure you it is safe to use our network.
Your online security is of the utmost importance to us and we employ industry best practices to ensure BGP security is enforced.
BGP hijacking is a relatively rare security risk which has recently been publicised by companies selling solutions for it, in order to promote their own technologies (in this case RPKI).
RPKI has, as far as we know, not yet been implemented by any ISP in the UK, and by only a handful of ISPs globally. It is currently only supported by a couple of hardware vendors for network routers, and not by the majority.
In line with other ISPs, we are closely following industry developments to ensure BGP security in the future, and we will continue to use best practices.
So please rest assured that you can continue to use your Hyperoptic service as normal.”


Mark is a professional technology writer, IT consultant and computer engineer from Dorset (England), he also founded ISPreview in 1999 and enjoys analysing the latest telecoms and broadband developments. Find me on X (Twitter), Mastodon, Facebook, BlueSky, Threads.net and Linkedin.




« Cityfibre’s 1Gbps FTTH Broadband Goes Live in Northampton UK









Comments are closed